● SYSTEM ONLINE Monday October 19, 2026 00:00:00.00
// LOG INTERCEPT: "Articles will be revealing in many aspect of information security and information technology in general,..."// LOG INTERCEPT: "If you want to be a professional in this field, a real security pro, a..."// LOG INTERCEPT: "The Illusion of Being “Connected” We built an internet that behaves like a crowded room..."// LOG INTERCEPT: "I have talked many times about management and why I believe a manager cannot be..."// LOG INTERCEPT: "There is a wrong perception of Cloud security among consumers of the Cloud solutions and..."
SYS.DATE: 2026.06.12 2 min read
The Wrong Path to Security

Running in Circles You are lost in a security rabbit hole, and you are not getting any closer to being secure. You think you are making progress, but you are not. You keep investing in products and services, yet your risk remains the same. The reason is simple: you are taking the entirely wrong route. […]
[ READ TRANSMISSION → ]
SYS.DATE: 2026.06.01 3 min read

Technology Is Not the Goal!

We’ve reached a point where people talk about technology as if it’s the destination (look what’s happening with AI these days). It is not! Technology is only useful when it serves a human purpose. Everything else is noisy shiny distracting, and completely disconnected from the real problems we face as a species. I’ve spent almost […]

[ READ TRANSMISSION → ]
SYS.DATE: 2026.05.28 2 min read

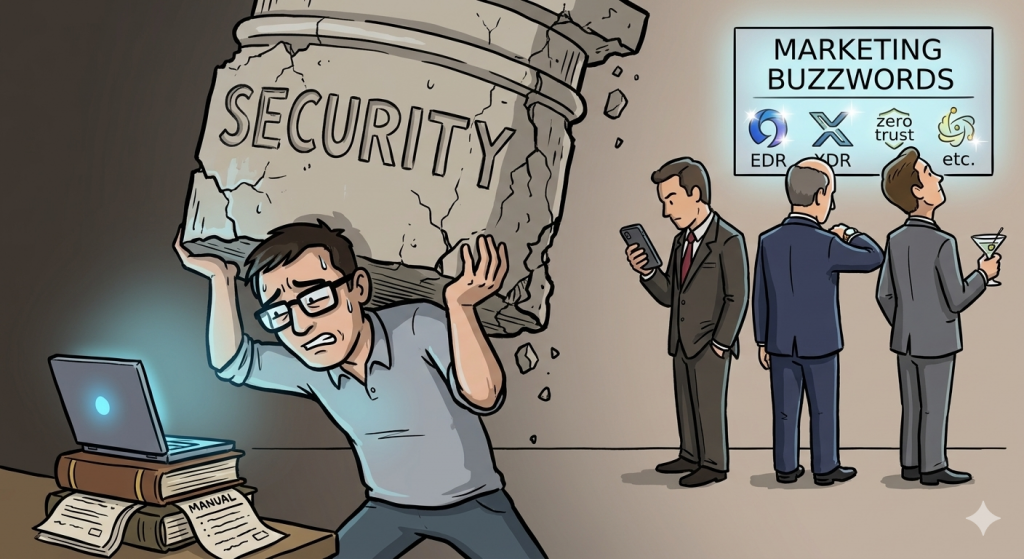
The Hollow Shell of Unsupported Security

The Myth of the Silver Bullet Too many organizations today are under the impression that a collection of marketing buzzwords, EDR, XDR, Zero Trust, NGF, and the rest, constitutes a valid security program. They treat these acronyms as a substitute for actual strategy, delegating the entire responsibility to a team while the leadership remains detached. […]

[ READ TRANSMISSION → ]
SYS.DATE: 2026.05.20 2 min read

When the Tool Starts Believing Itself

The new illusion These days, the industries have a new religion: Agentic AI will fix everything! People talk as if tools have finally replaced thinking, planning, and responsibility. But the fantasy is the same as before, only louder. A tool can act. A tool can automate. A tool can even decide within a narrow frame. […]

[ READ TRANSMISSION → ]
SYS.DATE: 2026.05.18 3 min read

The Management Flaw Nobody Wants To Admit

Controversial // IT Management // Leadership // May 18, 2026

The Problem Is Not The Worker/Employee One time I discussed this matter in depth: Because most managers have never done the things they are asking others to do. That is the root of the problem. If somebody never experienced the work themselves, they have no real understanding of: So what happens? Random and completely arbitrary […]

[ READ TRANSMISSION → ]
SYS.DATE: 2026.04.24 2 min read

Do You Still Need Assembly?

Artificial Intelligence // Coding // April 24, 2026

The Short Answer Yes, but not for the same reasons we once did. These days, learning assembly isn’t about speed or necessity. It’s about understanding the machine beneath the abstraction. The Shift Back in the day, you wrote assembly because it was fast, direct, and satisfying. You didn’t need a compiler, you were the compiler. […]

[ READ TRANSMISSION → ]
SYS.DATE: 2026.04.17 3 min read

AI‑Washing in Cybersecurity

The market is in a phase where “AI” has become a marketing label rather than a technical description. Vendors stretch, exaggerate, or outright misrepresent what their products actually do, and the industry is quietly normalizing it. I’ve personally seen platforms confidently branded as “AI‑driven” when, under the hood, they are nothing more than deterministic playbooks, […]

[ READ TRANSMISSION → ]
SYS.DATE: 2026.03.07 3 min read

The Compliance Misinterpreted!

When “Check-the-Box” Fails Most companies today live in a dream world. They think that passing an audit or getting a certification means their software is secure. It does not. Regulatory compliance is not security, it is just paperwork. If your software is built on a foundation of neglect, it is already waiting to be exploited. […]

[ READ TRANSMISSION → ]
SYS.DATE: 2026.02.11 7 min read

The One Question That Separates the Good Vendors from the Dangerous Ones

I have spent years watching organizations waste thousands of hours on vendor security assessments that produce nothing but noise. They send out hundred-question questionnaires. They demand SOC 2 reports. They ask for ISO certifications. They request NIST maturity scores. And at the end of all that paperwork, they still have no idea if the vendor […]

[ READ TRANSMISSION → ]
SYS.DATE: 2026.02.07 7 min read

A Good Manager vs a Political One

Controversial // Leadership // Technology // February 7, 2026

I have talked many times about management and why I believe a manager cannot be truly effective if s/he does not understand the details of what they are managing, but there is another part of management that I think is equally important and rarely discussed honestly: “Politics“. I grew up in a culture where keeping […]

[ READ TRANSMISSION → ]
SYS.DATE: 2026.01.03 2 min read

The Confusion Between Scanning and Testing

The Illusion of Coverage Many still confuse vulnerability scanning with penetration testing.They sound similar. They are not. One is automated noise.The other is a human discipline. A scan gives you a list.A pentest gives you a story. Lists are comfortable. They feel complete.Stories are uncomfortable. They expose what actually breaks. Most organizations choose comfort. Getting […]

[ READ TRANSMISSION → ]
SYS.DATE: 2025.12.26 2 min read

AI vs ML and why it is important in cybersecurity

we love buzzwords in cybersecurity. every few months the industry discovers a new shiny acronym, slaps it on the same old product, and suddenly we’re all supposed to believe the world has changed. now the magic word is “AI.” everything is “AI-powered,” “AI-enhanced,” “AI-driven.” but when you look under the hood, most of these so‑called […]

[ READ TRANSMISSION → ]