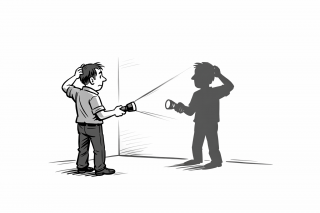
The illusion of independence
In 2025, the industry still repeats the same mistake: letting the same hands build the system and then “validate” it. That is not validation. That is self‑comfort.
A consultant who deploys your environment cannot be the one who tests it. A builder cannot be the judge of their own shortcuts. A shadow cannot audit itself.
When someone builds your cloud environment and returns with a “security report,” the first question is simple: Did they even read cloud vendor’s advisories?
No hardening. No baseline. No alignment with any defensible standard?
They deployed an environment they did not understand, and then “tested” it with tools they did not control.
“Trusting that process is like letting the painter inspect the cracks they painted over.”
You cannot trust a consultant who does not even align with your baseline. You cannot trust a report that ignores your operational reality. You cannot trust a process that was never designed to protect you.
The real issue
These are not consultants. They are task‑takers. They want to finish the job, not understand the environment.
A real consultant challenges you. A real consultant refuses to test what they built. A real consultant knows the difference between scanning and testing. A real consultant does not hide behind tools.
The industry is full of mid‑level operators pretending to be adversaries. Your job is to see through the performance.
You cannot trust a security assessment performed by the same entity that built the environment.”
Hope that makes sense!